What you see in the portal
Your login shows every protected computer, its antivirus and firewall status, and any open incident, updated every hour. No waiting for a quarterly review to find out where you stand.
Client portal sign-in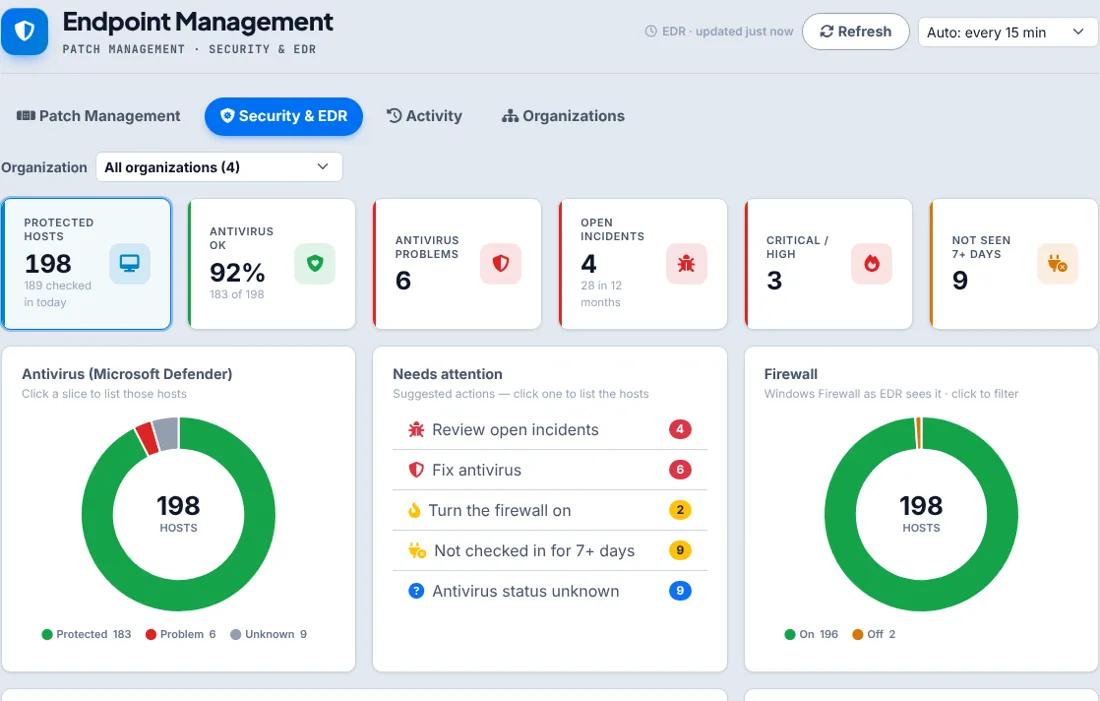
Huntress on every computer and server, watched around the clock by real analysts. Threats are isolated, a ticket opens, and you see it all in your portal.
From $32 per device per month, patching included.
Detection and response on every Windows and Mac computer and every server.
Real analysts triage every alert, day and night, so you are not woken up by false alarms.
A compromised computer is cut off from the network until it is clean.
Finds attackers hiding in startup items and scheduled tasks before they launch ransomware.
The antivirus you already have, kept on, up to date and watched.
Protected devices, incidents and what was done, ready for your board or insurer.
The same five steps, whether it happens at 2 p.m. or 2 a.m.
The Huntress agent flags suspicious activity on a device.
A Huntress analyst confirms whether it is real, usually within minutes.
Confirmed threats are contained: the device is isolated and the foothold removed.
A Support Desk ticket opens automatically and our team takes it from there.
You get a plain-English summary, and the incident shows in your portal.
Your login shows every protected computer, its antivirus and firewall status, and any open incident, updated every hour. No waiting for a quarterly review to find out where you stand.
Client portal sign-in
Huntress EDR with the 24/7 SOC, automated patching, remote monitoring, DNS filtering and your portal dashboard.
Everything in Managed EDR & Patching, plus business-hours helpdesk support for your staff.
Usually not. Huntress manages Microsoft Defender, which is already built into Windows, and adds detection and response on top of it. If you pay for another antivirus product today, we will tell you whether keeping it adds anything.
The Huntress SOC investigates around the clock. If a computer is compromised it can be isolated from the network right away, so the threat cannot spread. A Support Desk ticket opens automatically and we follow up with you first thing.
No. The agent is lightweight and does its heavy analysis in the cloud. Most staff never notice it.
Yes. Windows, macOS and Windows Server are covered. Servers are priced separately on the pricing page.
Most insurers now ask whether you have EDR on every endpoint and who monitors it. Managed EDR with a 24/7 SOC answers that question, and the monthly report is the evidence.
Yes. The Managed EDR & Patching package is built for that: we run the security tools and the SOC escalations, your IT person keeps everything else. Support Care adds our helpdesk if you want it later.
Tell us how many computers and phones you have. We will show you what is unprotected today and what it would cost to fix.
Book a free audit